
Cyber café operators across Kenya will be required to collect and retain customer records for at least three years under new regulations aimed at strengthening oversight of public internet access points and helping authorities combat cybercrime.
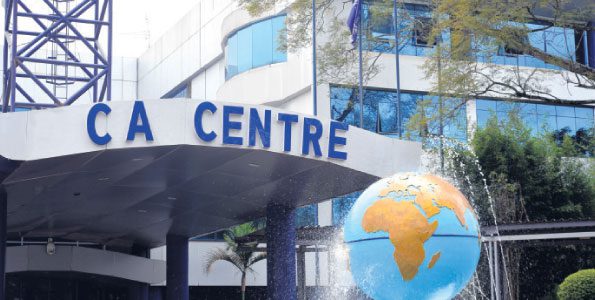
The regulations, which take effect on August 14, require operators to register customers, maintain session logs and provide records when requested during inspections, audits or investigations by the Communications Authority of Kenya (CA).
The new rules require cyber cafés to record a customer’s name, identification number, the computer terminal used and the time a session begins and ends. Operators will also be expected to issue receipts and keep the records safely for a minimum of three years.
New Cyber Café Regulations
The regulations come amid growing concerns over cybercrime, including online fraud, identity theft, phishing attacks and other digital threats affecting individuals, businesses and public institutions.
CA says stronger controls are necessary to help investigators trace activities that may originate from public access facilities.
Also Read: Dollar Check: Kenya Shilling Stays Stable as Forex Reserves Hit $15.2 Billion
The authority will also have powers to access premises, systems, equipment and records belonging to licensed operators when carrying out inspections or investigations.
However, the regulations do not require cyber cafés to keep records of customers’ browsing histories.
Instead, operators will retain basic session logs showing which registered customer used a specific computer terminal and at what time.
The latest requirements follow a regulatory review process that began several years ago.
Earlier proposals by the Communications Authority sought to tighten controls on cyber cafés through measures such as customer identification, record keeping, logging software and surveillance systems.
The regulator argued that the large number of cyber cafés operating across the country presented oversight challenges that needed to be addressed.
Under the current framework, cyber cafés have been licensed under the Public Communication Access Center category.
However, the regulator proposed changes designed to bring internet browsing facilities under stricter licensing conditions while ensuring compliance with security and consumer protection standards.
The CA maintains that the measures are aimed at addressing challenges associated with anonymous use of shared computers and internet connections.
By linking users to specific terminals and session times, investigators may find it easier to establish who accessed a particular machine at a particular time if a cybercrime incident is reported.
Kenya’s Escalating Cyber Threat Landscape
Kenya has experienced a sharp increase in cyber threats over recent years as more services, payments and government functions move online.
Also Read: Registrar of Political Parties Announces 365 Jobs Ahead of 2027 Elections: How to Apply
Data from the Communications Authority of Kenya (CA) shows that the National Kenya Computer Incident Response Team Coordination Center (KE-CIRT/CC) detected 3.37 billion cyber threat events between January and March 2026 alone.
System attacks accounted for more than 3.23 billion incidents, while malware, brute-force attacks and web application attacks all recorded significant increases.
Financial losses linked to cybercrime have also risen sharply.
According to the Africa Cybersecurity Report 2024/2025, Kenya lost an estimated Ksh29.9 billion ($230 million) to cybercrime and cyber incidents, with financial services, government agencies and telecommunications firms among the most targeted sectors.
Payment fraud, online fraud, email fraud, phishing and ransomware attacks were identified as major drivers of the losses.
Mobile money users have increasingly become targets of cybercriminals. An INTERPOL assessment released in 2026 reported that Kenyans lost an estimated Sh491.6 million through SIM-swap fraud in 2025.
The report noted a 327 percent increase in SIM-swap cases and more than 123,000 fraudulent SIM cards linked to criminal activity.
Growing reliance on mobile banking, digital payments, e-government services and cloud-based systems has expanded opportunities for criminals to exploit weak passwords, stolen credentials, phishing schemes and software vulnerabilities.
Follow our WhatsApp Channel and X Account for real-time news updates.